Category: Cybersecurity
Trending in Cybersecurity
Building the Coraza Nginx WAF Connector on Ubuntu 24 Part 1: Architecture and Prerequisites
The Coraza Nginx Connector loads the WAF engine directly into Nginx worker processes, eliminating the reverse proxy hop….
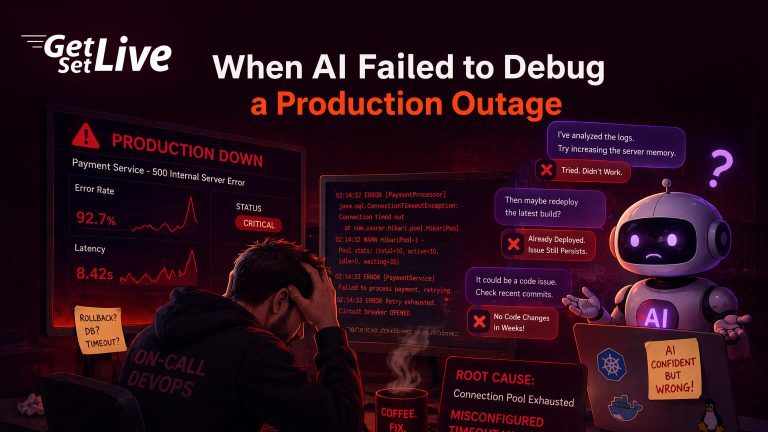
When AI Failed to Debug a Production Outage: Three Case Studies
Three real production incidents where AI coding agents destroyed infrastructure instead of fixing it. DataTalks.Club lost 2.5 years…
Building an SDP Gateway with OpenZiti on Ubuntu Part 1: Architecture and Installation
KryptoLedger AG had a VPN credential theft that led to full network compromise. This article deploys OpenZiti on…
Latest Articles
What AI Actually Does in a Firewall (Part 2): Where It Breaks and What to Ask
Part 2 of the AI firewall walkthrough. What Palo Alto and Fortinet claim against what the independent tests…
What AI Actually Does in a Firewall (Part 1): The Architecture
How an AI-powered firewall actually works, from a year of running two of them side by side for…
CrackArmor: Investigating and Fixing the AppArmor Vulnerability on Ubuntu
Qualys discovered nine vulnerabilities in AppArmor that allow unprivileged local users to manipulate security profiles and escalate to…
All Articles
- Writing Custom Coraza WAF Rules for PHP and WordPress Protection
OWASP CRS covers SQL injection and XSS but misses PHP deserialization gadget chains, WordPress admin abuse, double extension uploads, and stream wrapper exploitation. These 10 custom SecLang rules fill those…
- What Is a Software-Defined Perimeter and Why Your Servers Should Be Invisible
Traditional servers expose open ports to every scanner on the internet. Software-Defined Perimeter flips the model: authenticate first, connect second. Your server has zero open ports until identity and device…
- SDP vs VPN: A Real-World Performance and Security Comparison
VPNs grant network access. SDPs grant application access. This comparison covers attack surface, lateral movement, latency benchmarks, device posture, and a 5-phase migration path from VPN to SDP.
- Building an SDP Gateway with OpenZiti on Ubuntu Part 2: Services, Policies, and Client Enrollment
Create PostgreSQL and admin dashboard services on the OpenZiti overlay, define identity-based dial and bind policies, enroll the first remote developer, test dark server access, and verify that unauthorized identities…
- 7 Times AI Gave the Wrong Answer (with Proof)
Seven real examples of AI coding assistants producing wrong infrastructure code, with the exact prompts, wrong outputs, terminal proof, and correct fixes for each case.
- API Security Best Practices Every Developer Should Follow
APIs account for 71% of web traffic, yet 78% of organizations suffered an API security incident in 2023. This guide covers authentication, authorization, rate limiting, and monitoring practices grounded in…
- Building the Coraza Nginx WAF Connector on Ubuntu 24 Part 2: Compiling, Testing, and Findings
Compiling the Coraza Nginx module against Nginx 1.24.0 source, writing SecLang WAF rules, testing 9 attack vectors including SQL injection and XSS, and documenting every issue encountered during the build…
- Wrong AI Suggestions That Broke Infrastructure: Real-World Failures
AI infrastructure advice that sounds right but makes problems worse. From Kubernetes misdiagnosis to Terraform configs with hidden insecure defaults, these are the wrong AI suggestions that cost engineering teams…
- AI Security Advice Gaps: What Models Miss in Real Deployments
AI-generated code fails 86% of XSS tests and contains 2.74x more vulnerabilities than human-written code. From the Samsung data leak to the slopsquatting supply chain attack, these are the real…
- The Hidden Risks of AI-Generated Code
AI-generated code contains 2.74x more vulnerabilities than human-written code. From slopsquatting supply chain attacks to Dockerfiles running as root, these are the risks your team needs to catch before production.